Written by Heather Cole, 02/26/2026
If you run IBM Planning Analytics or IBM Cognos Analytics on Cloud, SOC 2 will matter the moment someone else asks about it.
That moment usually looks like this:
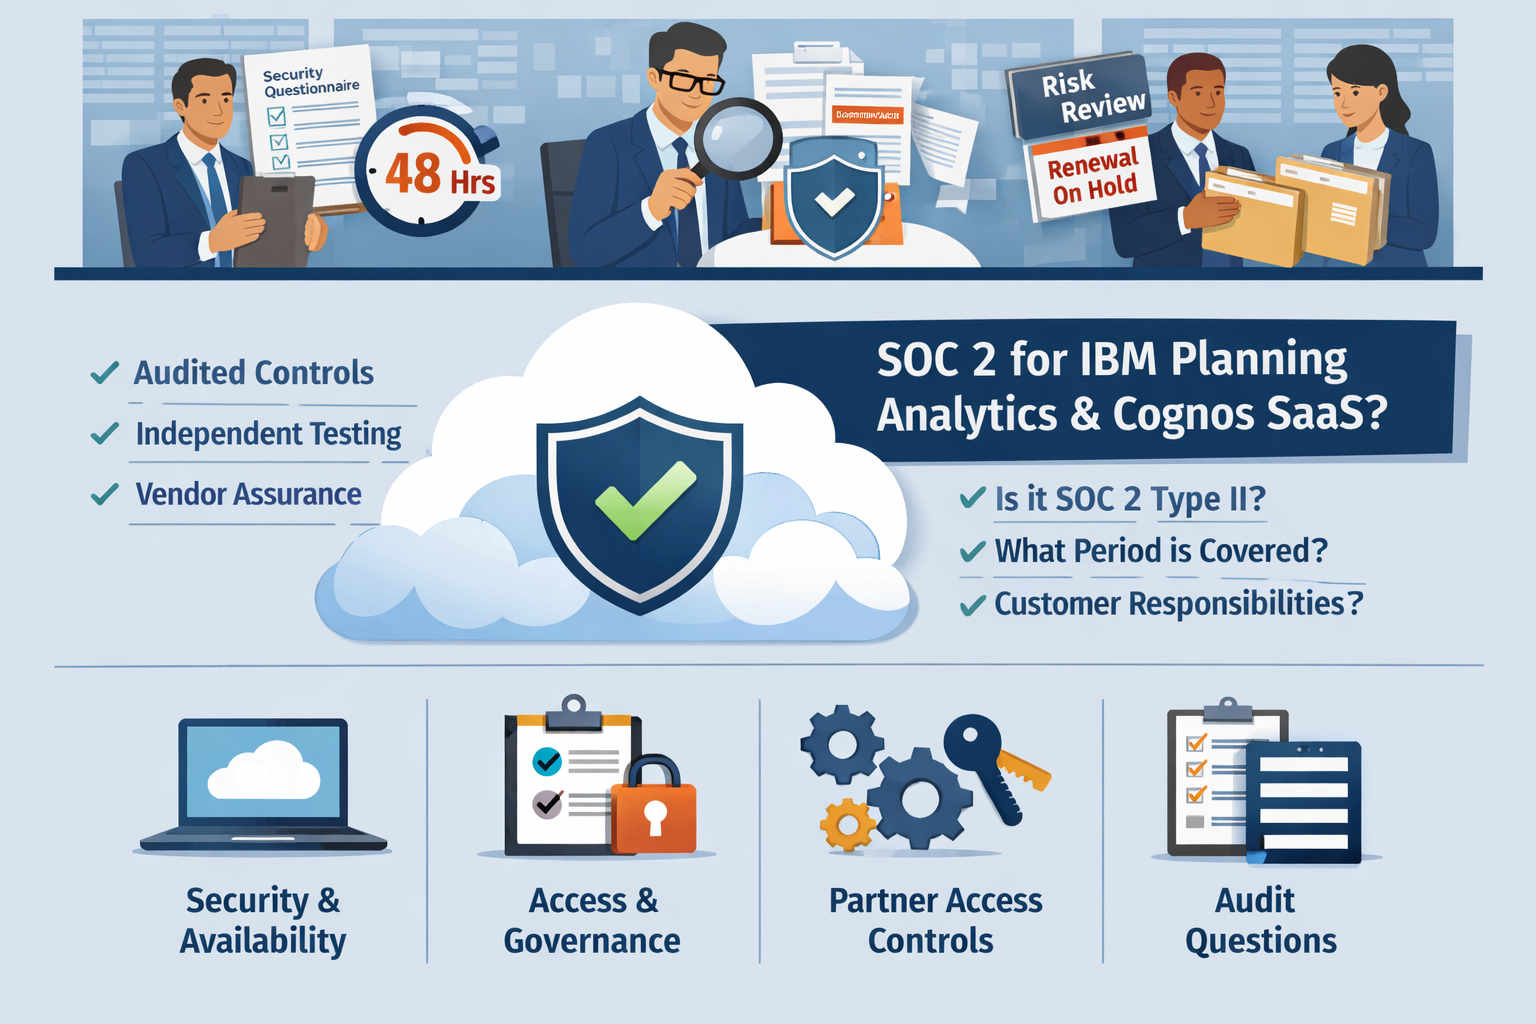
- Procurement sends a security questionnaire and wants answers in 48 hours
- Internal audit asks for proof your planning data is protected in the cloud
- A vendor risk review stalls renewal or expansion until you produce documentation
This post is for organizations already on IBM Planning Analytics and Cognos SaaS, or actively considering the move to IBM Cloud.
This is not for companies trying to become SOC 2 certified themselves.
By the end, you’ll know:
- what SOC 2 report to request and why
- what “in scope” actually means for Planning Analytics and Cognos SaaS
- what IBM covers vs what you still own as the customer
- the questions that prevent last minute audit fire drills
What SOC 2 Is
SOC 2 is an AICPA framework used to evaluate how service organizations protect customer data, typically across:
- Security
- Availability
- Confidentiality
- Processing Integrity
- Privacy
Most customers request a SOC 2 Type II report because it demonstrates controls are not only designed, but operating effectively over a period of time.
For cloud customers, SOC 2 is not paperwork. It’s assurance.
Why SOC 2 Matters for IBM Planning Analytics and Cognos SaaS
When you run Planning Analytics or Cognos in the cloud, your planning and reporting data lives in a platform IBM hosts and operates.
That means IBM maintains SOC 2 reporting for the relevant cloud services. For clients, it generally translates into three practical outcomes:
- your environment runs on an audited control framework
- controls are tested regularly and independently
- vendor risk conversations get easier when you can show evidence
Important distinction: this is different for on premises deployments. If you run Planning Analytics or Cognos on premises, IBM is not hosting or operating your environment, so you would not request a SOC 2 report from IBM for that deployment.
The Questions to Ask Internally
When procurement or audit asks for SOC 2, these are the questions that matter:
- Which SOC 2 report applies to my service?
Planning Analytics SaaS and Cognos SaaS may map to different IBM cloud service documentation. - Is it SOC 2 Type II and what period does it cover?
If the report window is outdated, it creates extra work during reviews. - What are the customer responsibilities (CUECs)?
Even in a SOC 2 audited cloud, customers still own things like role design, access governance, and internal processes. - How is partner access handled and controlled?
If a partner supports your environment, procurement and audit will often ask: who can access what, how is it approved, and how is it logged?
These questions are the difference between “approved” and “follow up required.”
Where Lodestar Fits
Lodestar does not issue SOC 2 reports. Those reports are issued by independent auditors and maintained by IBM for its cloud services.
We can help you request your SOC 2 reports from IBM.
As an IBM partner, Lodestar helps clients:
- Implement and upgrade IBM Planning Analytics and Cognos SaaS environments
- Migrate on-prem to the cloud including license migrations
- Understand how vendor access and system administration are managed
IBM provides the secure cloud foundation. Lodestar helps you run on it responsibly and prove it when asked.
If you are a Lodestar client and need access to IBM’s SOC 2 documentation for your Planning Analytics or Cognos SaaS environment, our team can help. We regularly assist clients with navigating IBM’s security and compliance materials and can guide you to the appropriate SOC 2 reports as needed for audits, vendor reviews, or internal risk assessments. Simply reach out to us at support@lodestarsolutions.com, and we’ll point you in the right direction.
Already on Cloud?
If you’re already running Planning Analytics or Cognos on Cloud, your SOC 2 assurance comes from IBM.
Your leverage point is everything around it:
- who has access
- how changes are controlled
- how governance works in practice when the questions arrive
Considering a Move to SaaS?
SOC 2 should be part of your decision criteria.
Moving to IBM Cognos SaaS or Planning Analytics Saas can reduce the on premises security burden, but it doesn’t eliminate governance. It shifts the shared responsibility model, and teams that understand that early migrate faster and with fewer surprises.
Next Steps
If you want to avoid the audit season scramble, here are two ways we can help:
- Option 1: Email us at support@lodestarsolutions.com to request your SOC-2 reports.
- Option 2: Book a free call with us here and we’ll walk through what to request, or to explore what moving to SaaS might look like for you.
- Option 3: Check out our website for more information https://lodestarsolutions.com/planning-analytics/